
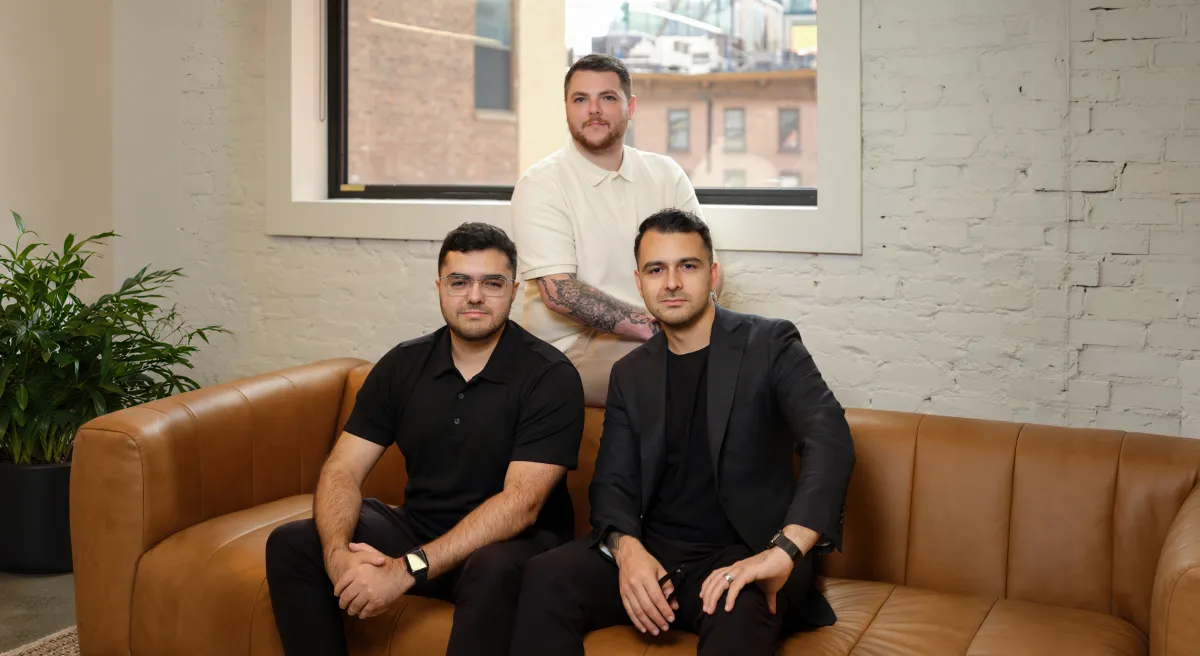
Comp AI, a cybersecurity and compliance startup, announced that it has raised a $34 million Series A round on Thursday. The round was led by Roo Capital and Grand Ventures.
—
**Key Takeaways:**
* **Significant Funding:** Comp AI has successfully closed a $34 million Series A round, bringing its total funding to $37.5 million, signaling strong investor confidence in its vision.
* **AI-Driven Compliance:** The startup is pioneering an “agentic platform” that leverages AI to automate traditionally tedious cybersecurity and compliance tasks, such as policy drafting and evidence collection for SOC 2.
* **Future-Proofing Security:** Comp AI’s solution emphasizes continuous monitoring and accountability for AI agents, directly addressing the evolving security risks and compliance demands of the rapidly expanding “agentic era.”
—
Comp AI Secures $34M Series A to Pioneer AI-Powered Compliance in the Agentic Era
In a significant stride for the cybersecurity landscape, Comp AI, an innovative startup dedicated to transforming compliance and security, today announced the successful closure of a $34 million Series A funding round. The substantial investment, co-led by Roo Capital and Grand Ventures, underscores a growing recognition of the critical need for advanced, AI-driven solutions to navigate the complexities of enterprise security. This latest infusion of capital brings Comp AI’s total funding to an impressive $37.5 million, positioning the company for accelerated product expansion and market penetration.
The Genesis: From Startup Setback to Compliance Breakthrough
The journey to Comp AI’s current success is rooted in the valuable lessons learned from a prior venture by its co-founders. Lewis Carhart (CEO), Claudio Fuentes (COO), and Mariano Fuentes (CTO) united their expertise after Carhart joined Claudio and Mariano at LeapAI, a workflow platform they had been building for several years. While LeapAI successfully scaled to over a million users, the team ultimately made the difficult decision to shut it down, unable to identify a sufficiently “sticky use case to warrant continued investment.”
This experience, however, proved to be an invaluable crucible. The founders emerged with a deeper understanding of building with Large Language Models (LLMs) and the paramount importance of targeting specific, acute pain points with their products. Crucially, their efforts to scale LeapAI to accommodate larger enterprise clients brought them face-to-face with the arduous, opaque, and incredibly time-consuming process of SOC 2 compliance.
“It’s a very obscure process,” Claudio Fuentes recounted, reflecting on the challenges they faced. “It took us a couple of months of doing things by hand, and the whole time it meant taking our eyes off building the product.” This firsthand encounter with the inefficiencies of traditional compliance sparked the idea for their next venture. This time, Lewis Carhart, whose initial insights helped define the problem, stepped into the CEO role, leading the trio toward a solution that would directly address the compliance quagmire they had personally experienced.
Solving a Pervasive Pain Point: The Compliance Conundrum
For countless software companies, achieving and maintaining security compliance — particularly certifications like SOC 2 — is not merely a regulatory hurdle but a direct enabler of business growth. As Carhart highlighted, “For a lot of software companies, security and compliance are directly tied to revenue.” He cited the common scenario where a potential customer might demand a SOC 2 report before finalizing a deal, making compliance a critical gatekeeper for enterprise sales and market expansion.
Yet, the traditional compliance process is anything but streamlined. It demands significant manual effort: drafting intricate security policies, meticulously collecting evidence from various internal systems, and constantly monitoring controls to ensure adherence. This often diverts valuable engineering and operational resources away from core product development, becoming a drain on both time and capital. The founders’ own struggle with SOC 2 became the cornerstone of Comp AI’s mission: to automate and simplify much of this traditionally manual, often repetitive work.
Comp AI’s Agentic Solution: Automating the Tedious, Empowering the Human
Comp AI is building what it calls an “agentic platform” designed to tackle the most laborious aspects of security and compliance work. At its core, the platform leverages advanced AI agents to perform tasks that would typically require extensive human intervention. This includes autonomously drafting company security policies tailored to specific requirements, intelligently collecting necessary evidence for security audits, and continuously monitoring whether a company is meeting its compliance controls in real time.
“What Comp AI automates is much of the work companies traditionally have to do around that process,” Carhart explained. The software acts as an intelligent assistant, helping companies meet and consistently maintain critical security requirements. Furthermore, Comp AI extends its capabilities to include AI-powered penetration testing, where “the platform proactively tests codebases and infrastructures for vulnerabilities,” adding another layer of proactive security.
Crucially, the founders emphasize that Comp AI is designed to augment, not replace, human expertise and independent audit review. “An agent might draft a policy, for example, but a person still reviews and approves it,” Carhart stated, underscoring the “human-in-the-loop” philosophy. Human workers are essential for onboarding the AI, supporting controls, and maintaining the agentic workflow. This approach ensures that as AI agents take on increasingly consequential actions, the necessary safeguards and human oversight increase accordingly, maintaining both efficiency and accountability.
Navigating the Agentic Era: Continuous Security in an AI-Driven World
The rapid proliferation and experimentation with AI technologies across industries are creating a new wave of security challenges. This “agentic era” — where AI agents increasingly interact with data, systems, and code — necessitates a paradigm shift in how security and compliance are approached. Traditional, static audits, conducted at specific intervals, are becoming insufficient in a world where system configurations, data access, and code deployments can change almost continuously.
“Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment,” Carhart illustrated. “The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward.” This gap in continuous visibility and immediate response is precisely where Comp AI aims to make a significant impact.
Mariano Fuentes elaborated on this forward-looking aspect: as companies adopt more AI, they need robust mechanisms to demonstrate precisely what an agent accessed, what it attempted to do, and whether it adhered to its predefined boundaries. “We’re building toward a security layer that can monitor and validate those kinds of risk more continuously as these systems evolve,” he affirmed. By focusing on permissions and accountability for AI agents, Comp AI is carving out a niche within the broader AI security and compliance market, addressing challenges that even established players like Vanta and Drata may not fully cover in this new, dynamic context.
Future Outlook: Scaling Innovation and Impact
With the fresh capital from its Series A round, Comp AI is poised for significant product expansion. The company plans to deepen its platform capabilities, refine its AI agents, and broaden the scope of compliance frameworks it can support. By building a robust and adaptive security layer, Comp AI aims to empower businesses to innovate with AI confidently, knowing that their security posture and compliance obligations are continuously monitored and proactively managed. The $37.5 million raised to date is a testament to the belief that Comp AI is not just solving today’s compliance problems, but also building the foundational security infrastructure for tomorrow’s AI-driven enterprises.
—
**Bottom Line:**
Comp AI’s substantial Series A funding marks a pivotal moment in the evolution of cybersecurity compliance. By leveraging a human-centric, agentic AI platform, the company is poised to alleviate the burdensome, manual processes that have long plagued businesses, while simultaneously addressing the novel security challenges presented by the widespread adoption of AI agents. In an increasingly complex digital landscape where compliance directly impacts revenue and innovation, Comp AI offers a timely and forward-thinking solution, promising greater efficiency, continuous security, and peace of mind for enterprises navigating the future of technology.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
{content}
Source:{feed_title}